Microsoft fixes Windows troubleshooting flaw found by Melbourne researcher
The Windows 11 vulnerability could give standard users full system access. Researcher Ben Wilson said Microsoft issued no CVE identifier.
By Quang Dinh
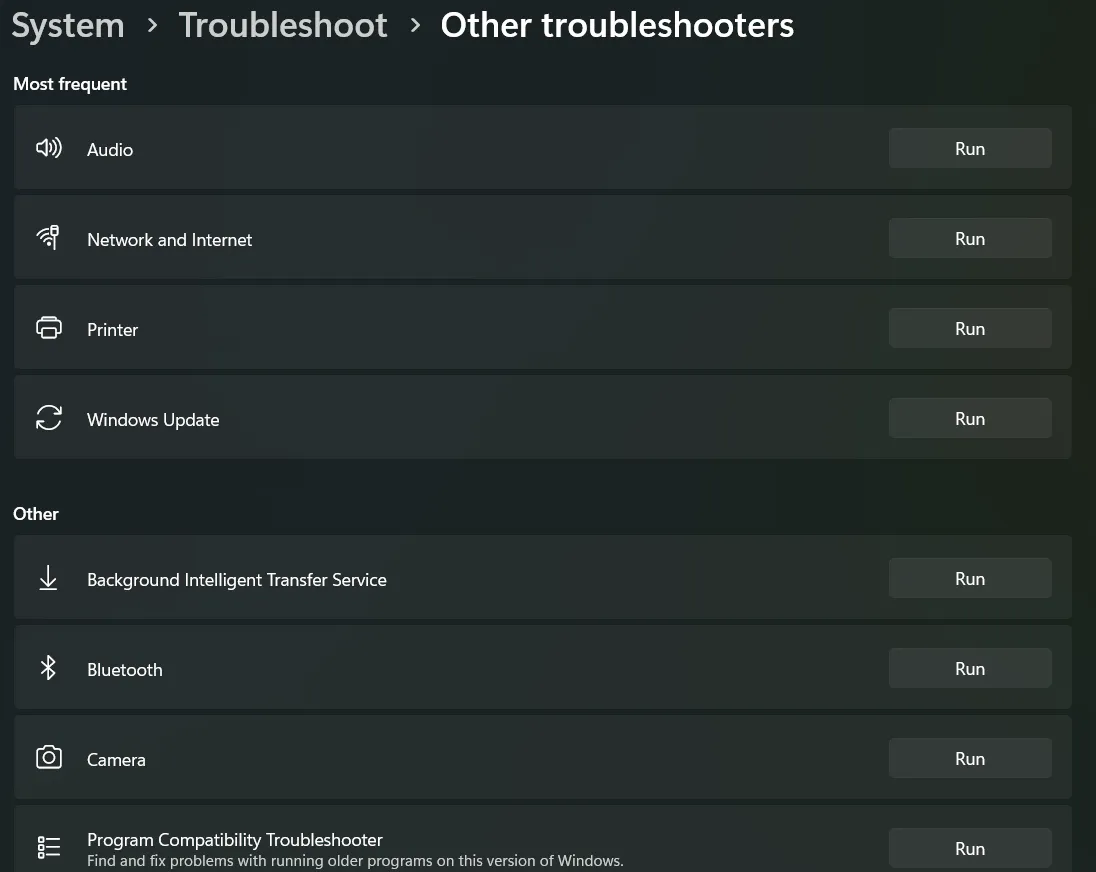
Microsoft has patched a Windows 11 troubleshooting vulnerability discovered by Melbourne security researcher Ben Wilson that could allow a standard user to gain complete control of a computer. The fix arrived around 1 September, without a CVE tracking identifier.
Wilson, of Tanto Security, found the weakness in a Get Help package that downloads and runs Microsoft’s Media Creation Tool, which builds Windows installation media. Get Help uses the Diagnostic Execution Service, or DiagSvc, to process troubleshooting scripts with SYSTEM privileges — the highest access level on Windows.
He found that Windows 11 allowed standard users to start DiagSvc without administrator approval. Two timing weaknesses in the package then enabled him to substitute his own program for the downloaded tool, causing it to run with SYSTEM access.
Wilson submitted his findings to the Microsoft Security Response Centre on 13 May. Microsoft verified the behaviour on 29 June and awarded a bounty the next day. Wilson said the patch changed a single script line to stop users taking control of the download folder, but he had not fully tested possible bypasses.
Microsoft paid Wilson US$8,000 for that discovery and another US$8,000 for a separate Outlook diagnostic flaw. A third vulnerability, involving Calendar diagnostics, remains in disclosure and unpaid. Wilson said Microsoft had issued no CVE identifiers for the flaws. He was not aware of any exploitation of the Media Creation Tool vulnerability in the wild.